
By the end of this guide, the reader should be able to:
- Explain network security in simple terms
- Understand the main security principles
- Recognize common network threats
- Understand firewalls, IDS, IPS, NDR, VPNs, NAC, segmentation, and Zero Trust
- Understand the basic architecture of a secure network
- Match common threats with appropriate security controls
- Identify weaknesses in their own network
- Build a basic security improvement plan
- Know what to monitor
- Know what to do if suspicious activity is detected
Network Security in Simple Terms
Network security is the combination of people, policies, processes, architecture, and technologies used to protect networks, connected systems, communications, and data against unauthorized access, misuse, disruption, modification, and attack. Explore our foundational Network Security hub and comprehensive Cybersecurity guides to see how these controls integrate across modern environments.
Quick Answer Box
- Knowing what devices, users, applications, and data exist
- Controlling who can access them
- Segmenting networks to limit unnecessary access
- Filtering malicious or unauthorized traffic
- Encrypting sensitive communications
- Detecting suspicious activity
- Fixing vulnerabilities and misconfigurations
- Monitoring networks continuously
- Responding to security incidents
- Recovering safely when something goes wrong
What Are Network Security Fundamentals?
Explain the subject from first principles.
Cover:
- What a computer network is
- What network security protects
- Internal vs external network threats
- Users, endpoints, servers, applications, network devices, cloud security resources, and data
- Why one security product cannot protect an entire network
- Why network security requires multiple defensive layers
Simple Example
User Identity → Authentication → Device Check → Network Access Control → Firewall → Segmentation → Application Access → Logging & MonitoringExplain what each layer is doing. This immediately helps the reader understand why network security requires several controls working together.
Why Is Network Security Important?
Answer the practical question: “What can happen if my network is not properly secured?”
Cover:
- Unauthorized access
- Data theft
- Account compromise
- Malware infections
- Ransomware
- Service outages
- DDoS attacks
- Lateral movement
- Data manipulation
- Business disruption
- Data privacy exposure
- Loss of critical systems
- Limit what compromised users/devices can reach
- Detect abnormal activity
- Protect sensitive traffic
- Maintain service availability
- Support recovery
The Three Core Principles of Network Security: CIA Triad
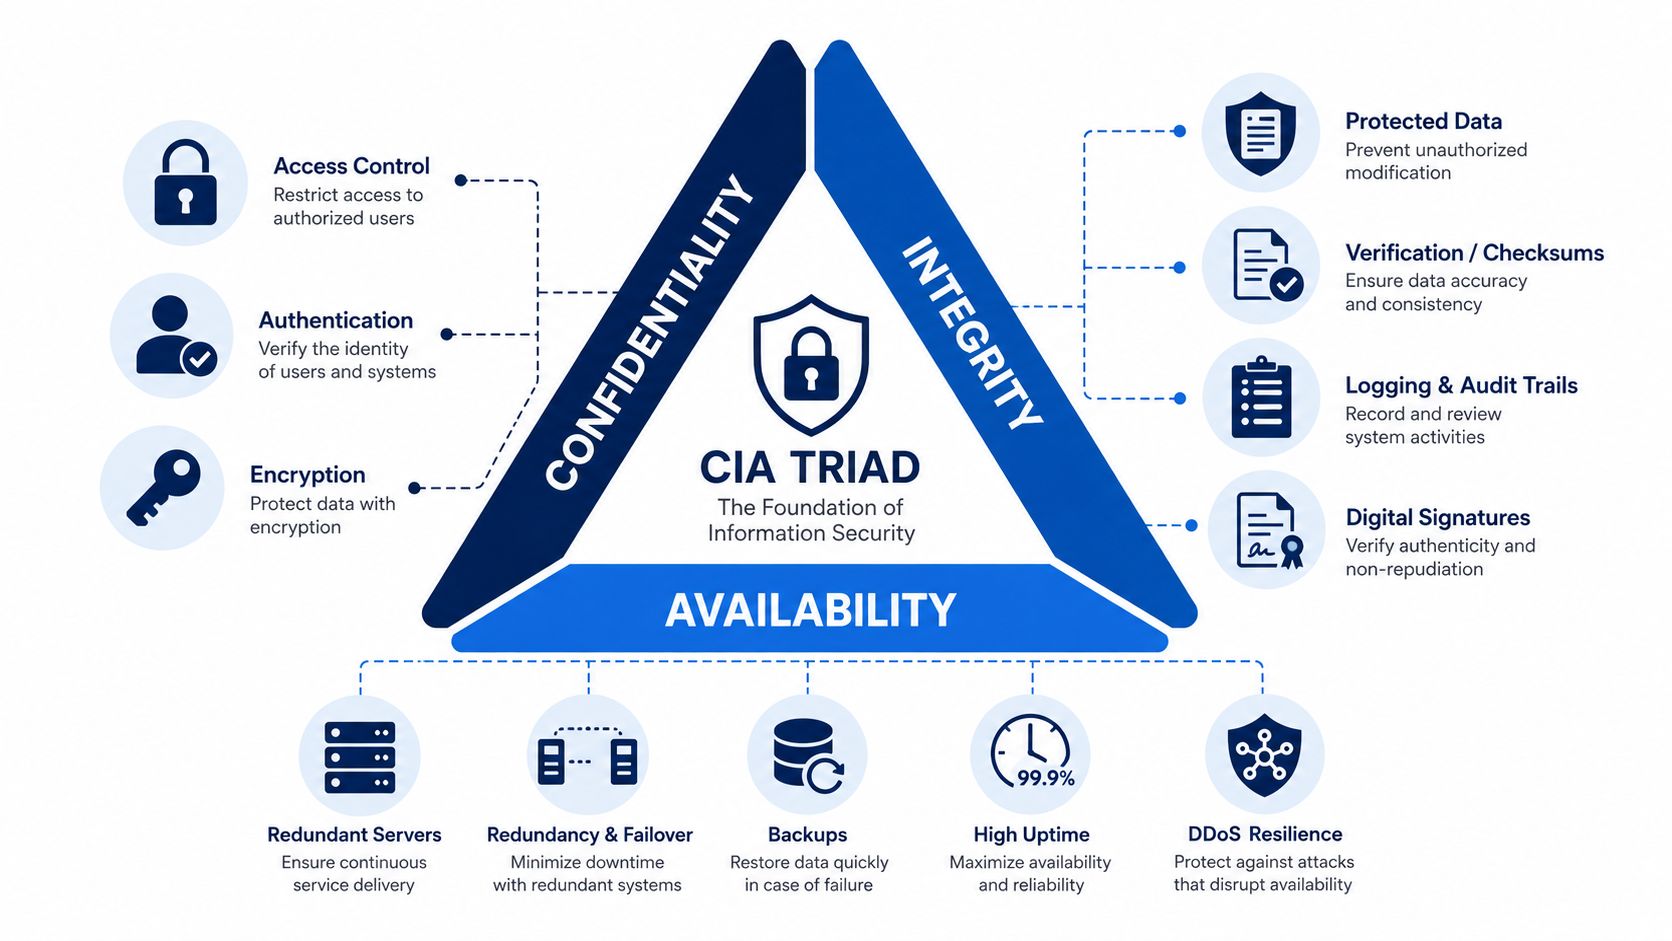
Confidentiality
Only authorized people and systems should be able to see sensitive information.
Controls may include:
- Authentication
- Access control
- Encryption
- Network segmentation
- VPN/ZTNA
- Data protection
Integrity
Information and systems should not be changed improperly.
Controls may include:
- Access permissions
- Cryptographic integrity checks
- Logging
- Change control
- Digital signatures
- Secure protocols
Availability
Authorized users should be able to access systems and data when needed.
Controls include:
- Redundancy
- DDoS protection
- Backups
- Failover
- Capacity planning
- Monitoring
- Incident response
Are There Really Five Pillars of Network Security?
Address this common search question carefully. There is no single universally accepted “five pillars of network security” model. Do not invent five pillars just to answer the keyword.
Clarify the two frameworks users often confuse.
Older NIST CSF 1.1
It organized cybersecurity into:
- Identify
- Protect
- Detect
- Respond
- Recover
Current NIST CSF 2.0
It uses six functions:
- Govern
- Identify
- Protect
- Detect
- Respond
- Recover
CISA Zero Trust Five Pillars
- Identity
- Devices
- Networks
- Applications and Workloads
- Data
Network Security vs Cybersecurity vs Endpoint Security
| Area | Main Focus | Example |
|---|---|---|
| Cybersecurity | Entire digital environment | Identity, cloud, apps, networks, data |
| Network Security | Network infrastructure and communications | Firewalls, IDS/IPS, NAC, segmentation |
| Endpoint Security | Individual devices | Laptops, desktops, phones, servers |
| Application Security | Software and applications | Secure coding, WAF, testing |
| Cloud Security | Cloud resources and services | IAM, cloud network controls, CSPM |
What Does a Secure Network Need to Protect?
A complete network-security plan should consider:
Users and Identities
Employees, administrators, contractors, customers, service accounts. Ongoing security awareness training ensures employees identify deceptive authentication threats.
Endpoints
Laptops, desktops, servers, phones, IoT devices.
Network Infrastructure
Routers, switches, firewalls, wireless access points, gateways.
Applications
Internal applications, SaaS tools, business applications, APIs.
Data
Customer records, credentials, financial data, intellectual property.
Cloud Resources
Cloud servers, storage, networks, workloads, containers.
Remote Connections
Remote employees, branches, vendors, third parties.
Essential Components of a Secure Network Infrastructure
Identity and Authentication
Explain:
- Unique user accounts
- Strong authentication
- MFA
- Privileged accounts
- Service accounts
- Authentication policies
Authorization and Least Privilege
Explain the difference between:
- Authentication: Who are you?
- Authorization: What are you allowed to do?
Introduce:
- Role-based access
- Least privilege
- Privileged access
- Access reviews
Give a real example.
Network Access Control (NAC)
NAC helps determine which users and devices can connect to network resources.
Discuss:
- Identity
- Device status
- Policy
- Access level
- Guest devices
- Corporate vs unmanaged devices
Firewalls: The First Major Traffic-Control Layer
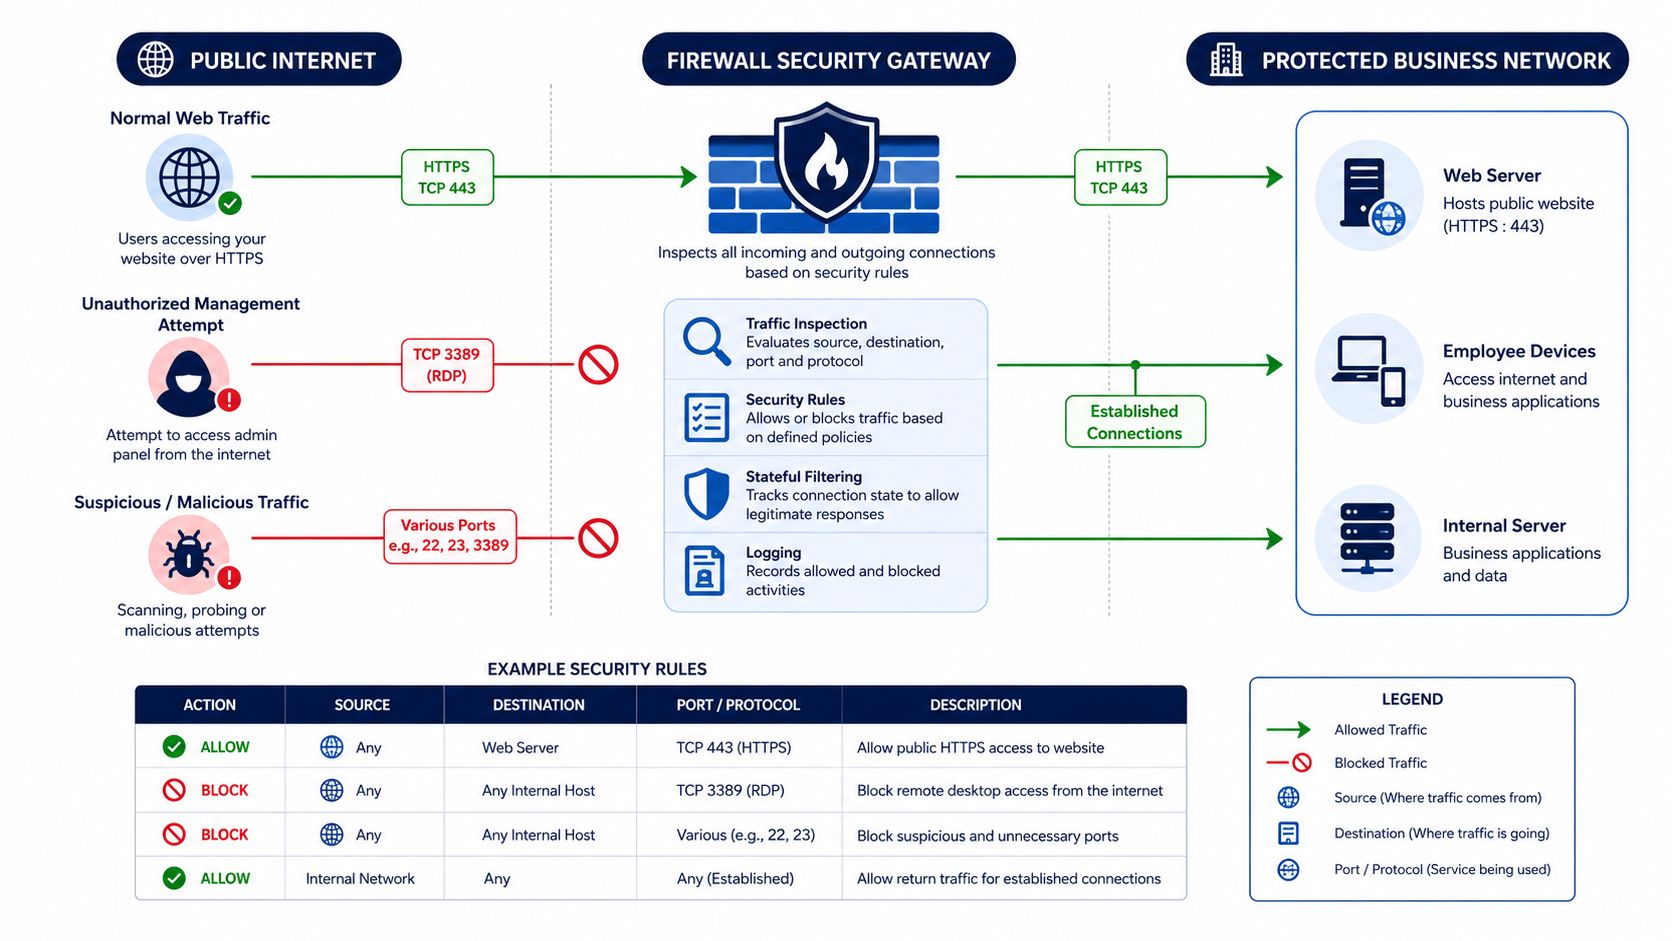
What does a firewall actually do?
A firewall examines network traffic and applies security rules to determine what should be allowed or blocked. You can generate hardened rule templates using our Firewall Configuration Assistant.
Cover major categories without turning the article into a firewall encyclopedia.
Packet-Filtering Firewalls
Basic decisions using information such as:
- Source IP
- Destination IP
- Port
- Protocol
Stateful Firewalls
Explain connection state and why context matters.
Next-Generation Firewalls
Explain conceptually:
- Application awareness
- Threat inspection
- IDS/IPS integration
- Advanced policy controls
Host-Based vs Network Firewalls
Explain when each applies.
Cloud Firewalls / Firewall as a Service
Briefly explain modern distributed environments.
Firewall Example
Blocked: Internet → Firewall → Unauthorized management connection → Blocked
Sample Firewall Policy Configuration
IDS vs IPS vs NDR: What Is the Difference?
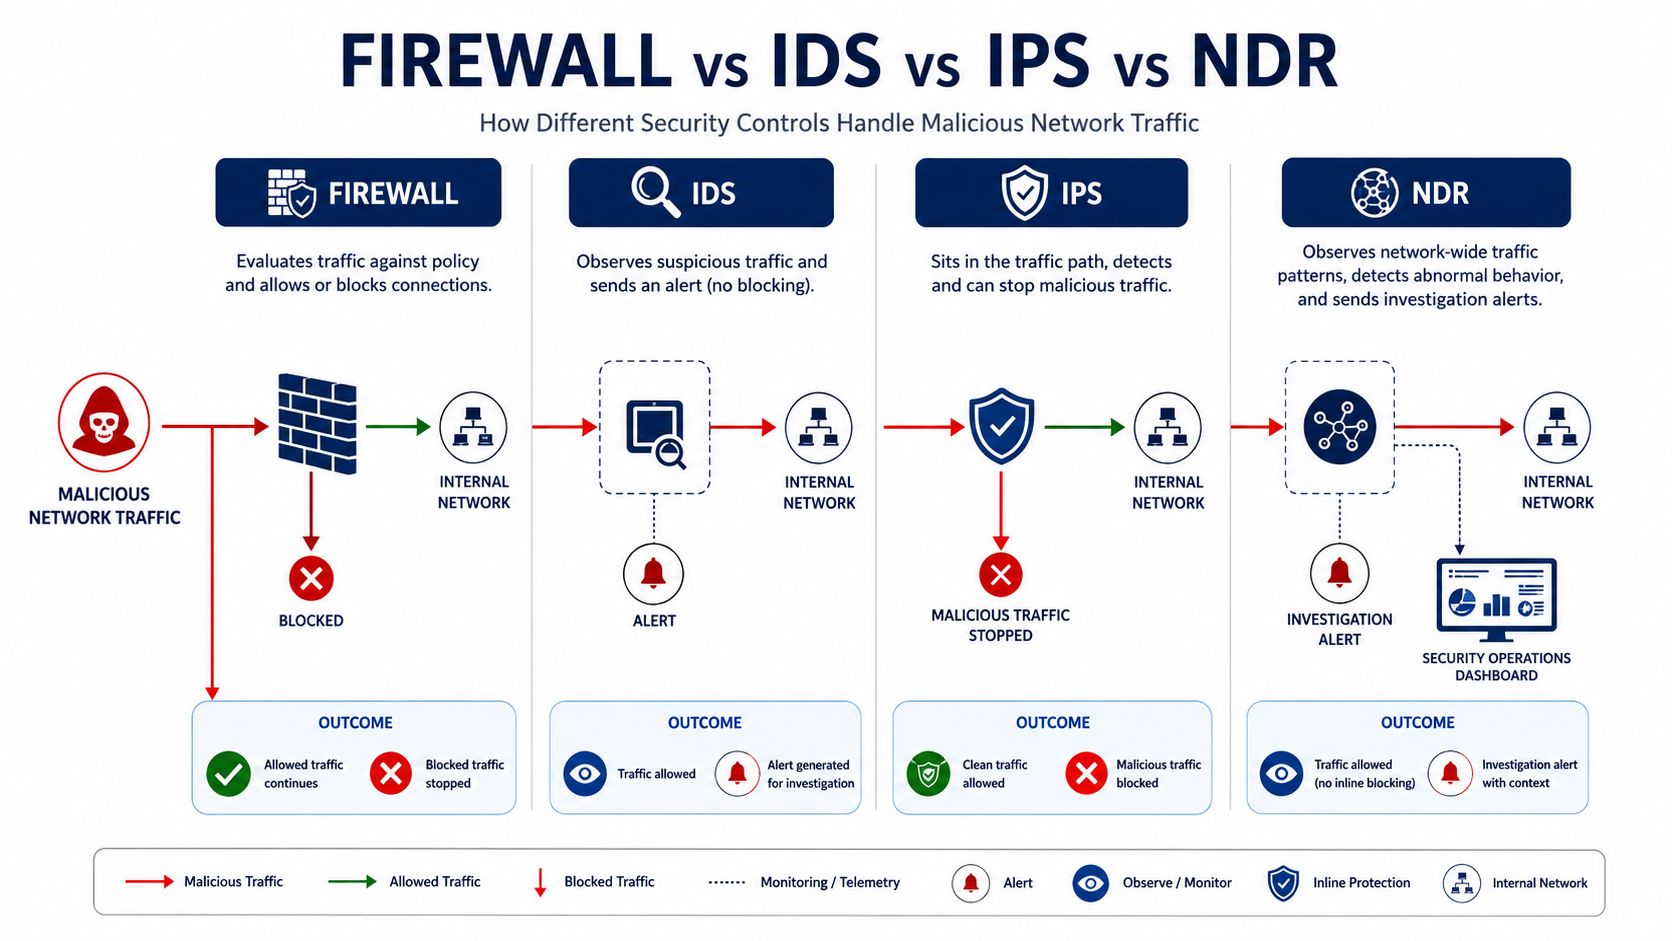
This section needs to completely answer a major user confusion.
Intrusion Detection System — IDS
Detects suspicious activity and generates alerts. It generally does not automatically block traffic simply because an alert was generated.
Intrusion Prevention System — IPS
Detects suspicious traffic and can actively block or prevent it.
Network Detection and Response — NDR
NDR analyzes network activity and behavior to help identify suspicious or abnormal patterns and support investigation and response.
Easy Comparison
| Technology | Main Job | Detects | Can Block? |
|---|---|---|---|
| Firewall | Control connections | Yes, based on rules/features | Yes |
| IDS | Identify suspicious activity | Yes | Usually no |
| IPS | Detect and prevent threats | Yes | Yes |
| NDR | Analyze network behavior | Yes | Depends on integration |
Do I Need IDS/IPS If I Already Have a Firewall?
Explain why firewall rules alone do not eliminate every threat and why multiple layers are used.
Network Segmentation: Stop One Compromise From Becoming a Full-Network Compromise
Instead of allowing every device to communicate freely with every other device, divide the network into security zones. Model your zone architecture with our Zero Trust Segmentation Planner.
- Guest Wi-Fi
- Employee Network
- Finance Network
- Server Network
- Management Network
Explain benefits:
- Limits lateral movement
- Protects sensitive systems
- Reduces unnecessary access
- Makes monitoring easier
- Can reduce the blast radius of compromise
What Is a VLAN?
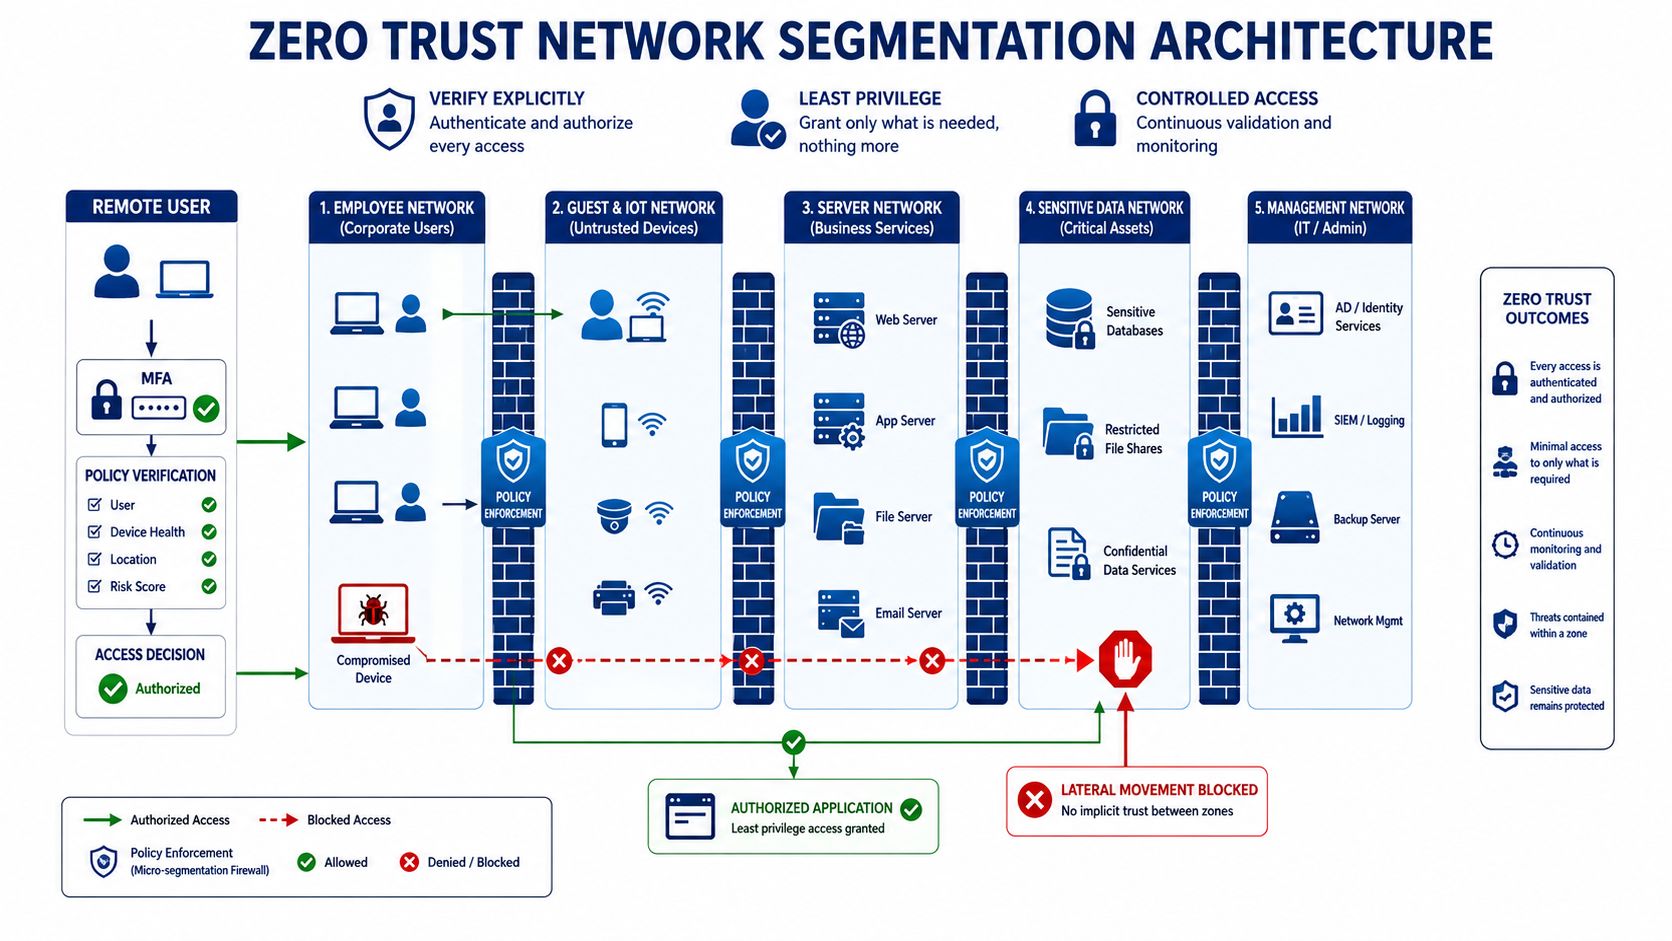
Zero Trust Network Security
Core idea: Do not grant access simply because a user or device is “inside” the network.
Access decisions should consider factors such as:
- Identity
- Device
- Requested resource
- Context
- Policy
- Risk
- Least privilege
Interactive Architecture Comparison: Flat vs Zero Trust Network
⚠️ Flat Network Perimeter (High Lateral Risk)
Once inside the perimeter, all endpoints communicate directly with critical databases, servers, and finance assets without internal inspection.
Cover:
- Continuous verification
- Least privilege
- Device trust
- Segmentation
- Application-specific access
- Logging and monitoring
Encryption and Secure Network Communication
Solve: “How do I stop someone from reading network traffic?” Test your domain encryption using our free SSL Certificate Checker and Security Headers Checker.
TLS
Protects many web and application communications.
VPN
Creates a protected connection between remote users/sites and a network.
IPsec
Can provide confidentiality, integrity, and authentication for IP communications.
SSH
Secure remote administration.
Examples: HTTPS instead of HTTP, SSH instead of Telnet
How Network Security Relates to the OSI Model
Do not turn this into an entire networking course. Use a compact security-focused table.
| Layer | Example | Security Relevance |
|---|---|---|
| L1 Physical | Cables, ports | Physical access |
| L2 Data Link | Ethernet, VLANs | Switch security, segmentation |
| L3 Network | IP, routing | ACLs, IPsec, routing security |
| L4 Transport | TCP/UDP | Port and connection filtering |
| L5–L7 | Sessions & applications | Application security, proxies, WAFs |
Are VLANs Layer 2 or Layer 3?
Is BGP Layer 2 or Layer 3?
Keep this answer short because BGP is not the article’s main topic.
Common Network Security Threats and Their Defenses
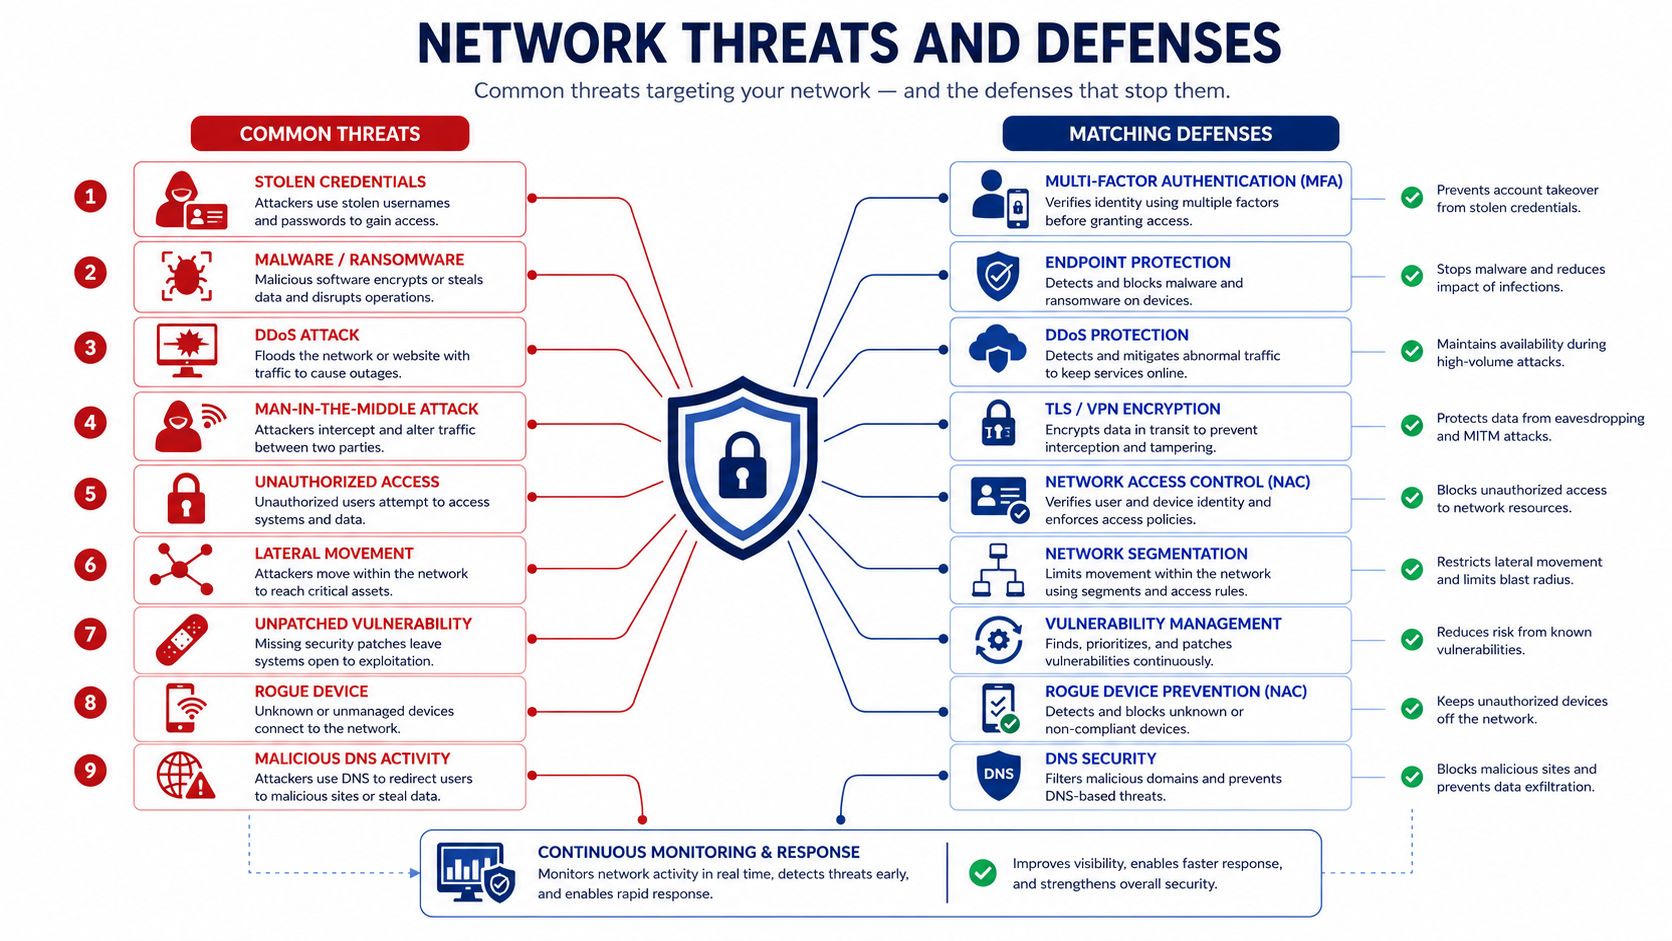
| Threat | What It Can Do | Key Defenses |
|---|---|---|
| Stolen credentials | Give attacker legitimate-looking access | MFA, identity monitoring, least privilege |
| Malware | Infect systems or steal information | Endpoint protection, filtering, segmentation |
| Ransomware | Encrypt systems and disrupt operations | EDR, patching, segmentation, backups |
| DDoS | Make services unavailable | DDoS protection, rate limiting, resilient architecture |
| Man-in-the-middle | Intercept communications | TLS, VPN, secure Wi-Fi |
| Unauthorized access | Enter restricted resources | Authentication, NAC, firewall |
| Lateral movement | Spread after initial compromise | Segmentation, Zero Trust, monitoring |
| Vulnerability exploitation | Abuse software/device flaws | Patching, vulnerability management |
| Misconfiguration | Accidentally expose systems | Hardening, review, configuration management |
| Insider misuse | Abuse legitimate access | Least privilege, logging, access review |
| Rogue devices | Join the network without approval | NAC, device inventory, segmentation |
| DNS attacks | Redirect or disrupt traffic | Secure DNS controls, monitoring |
The reader should be able to look at the problem and immediately see the relevant defense.
Vulnerability Management and Patch Management
Answer: “What happens after vulnerabilities are discovered?” Assess your operational readiness with our Vulnerability Management Checklist and Network Vulnerability Management Assessment.
Explain the lifecycle:
Discover → Assess → Prioritize → Remediate → Verify → Monitor
Cover:
- Vulnerability scanning
- Risk-based prioritization
- Critical patches
- Internet-facing systems
- Routers/firewalls
- Unsupported devices
- Configuration vulnerabilities
- Verification after remediation
Secure Configuration and System Hardening
- Change default passwords
- Remove unused services
- Disable unnecessary ports
- Use secure protocols
- Restrict administrative interfaces
- Remove unused accounts
- Apply security updates
- Protect management access
- Keep configuration backups
- Review firewall rules
Network Monitoring, Logging and Threat Detection
Answer: “How will I know if someone has compromised my network?” Explore recommended platforms with our Network Security Monitoring Tools guide.
Explain what should be monitored:
- Authentication failures
- Administrative logins
- New devices
- Firewall events
- IDS/IPS alerts
- DNS activity
- Traffic anomalies
- Unexpected outbound connections
- Configuration changes
- Privilege changes
- Access to sensitive systems
How Firewalls, IDS, IPS, NDR and SIEM Work Together
Use a simple flow:
Internet Traffic → Firewall → IDS / IPS → Network Segments → Endpoints / Servers
At the same time:
Firewall + IDS/IPS + Authentication + Servers + Endpoints → Logs → SIEM / Monitoring
Endpoint Security and Network Security
Cover:
- Antivirus
- EDR
- Host firewall
- Device encryption
- Patching
- Device management
Email and DNS Security
Email Security
Verify protocols with our Email Security Checker:
- Phishing filtering
- Malware filtering
- Authentication controls
- User awareness
DNS Security
Perform live checks with our DNS Security Checker and DNS Lookup tool:
- Malicious-domain blocking
- DNS monitoring
- Secure configuration
Explain why these services often become part of the overall defensive architecture.
Wireless Network Security
Audit your Wi-Fi configuration with our Wi-Fi Security Recommendation Tool:
- Strong Wi-Fi encryption
- Separate guest networks
- Secure administrative credentials
- Disable insecure configurations
- Keep access points updated
- Avoid sharing one network for every type of device
- Monitor unauthorized access points
Remote Access Security
Answer: “How should remote employees safely access company resources?”
- MFA
- VPN
- ZTNA
- Device checks
- Least privilege
- Logging
- Session controls
- Managed devices
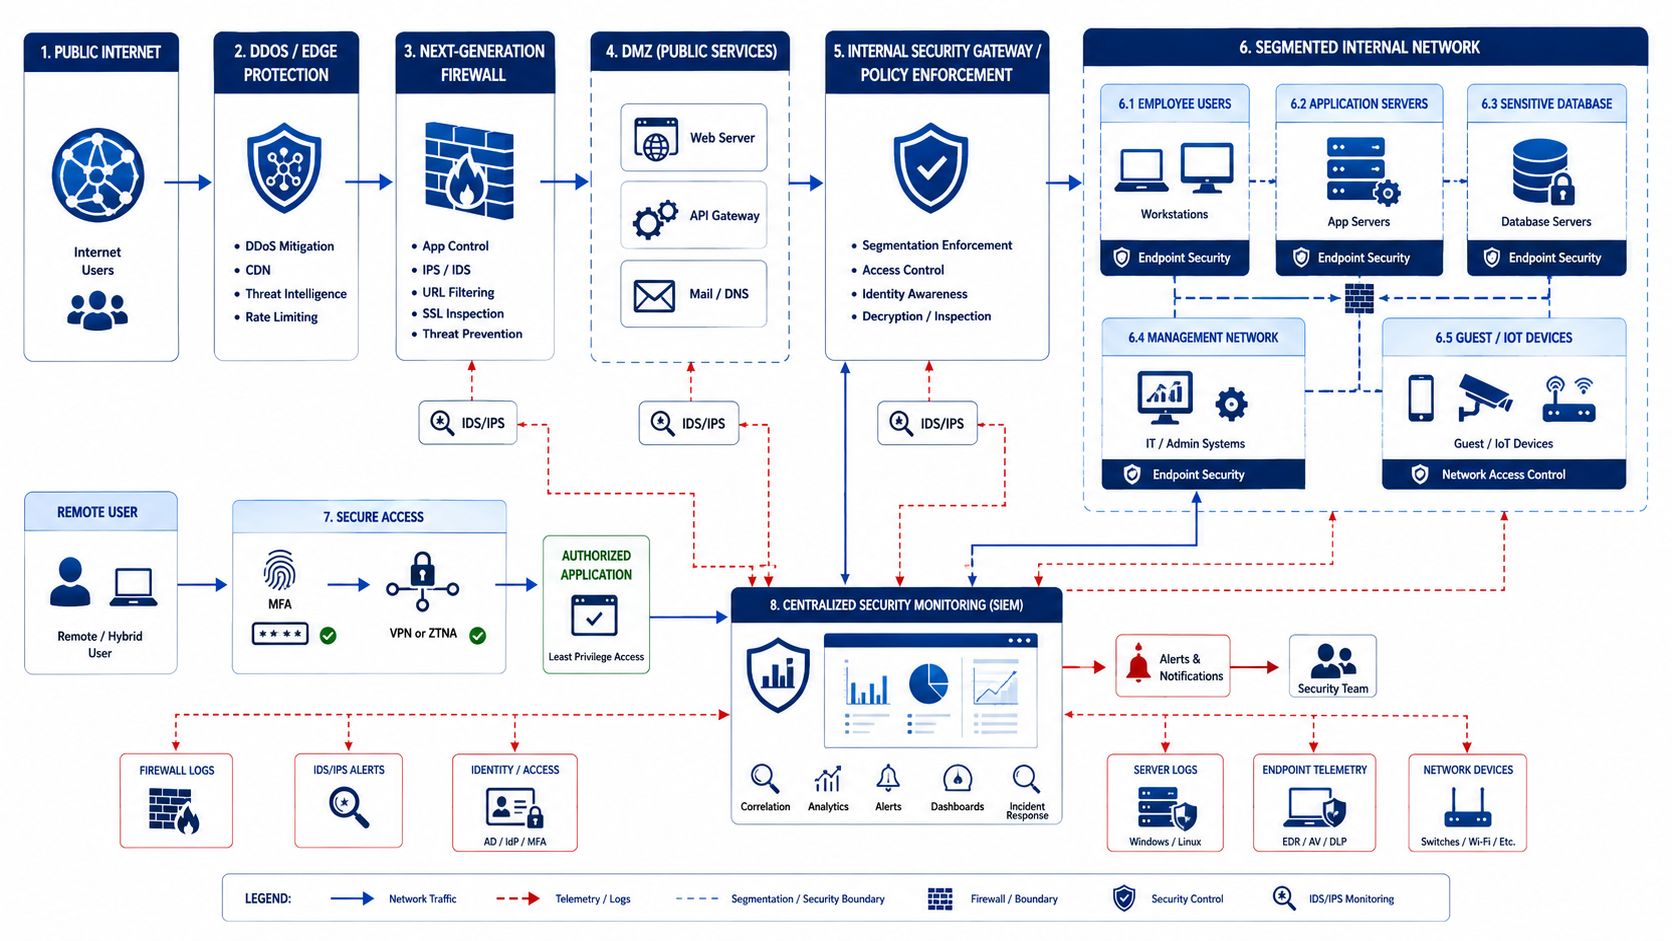
Secure Network Architecture: A Practical Example
Internet → DDoS / Edge Protection → Firewall / Secure Gateway → DMZ → Internal Firewall / Policy Enforcement → Segmented NetworksZones:
- User Zone
- Server Zone
- Sensitive Data Zone
- Management Zone
- Guest/IoT Zone
Remote User → MFA → VPN/ZTNA → Authorized ResourceSecurity telemetry:
Firewalls + IDS/IPS + Endpoints + Servers + Identity → Central Logging / SIEM / Monitoring
Explain why sensitive assets should not sit inside one completely flat network.
Architecture Diagram Gallery
What Is a DMZ?
Examples:
- Public web servers
- Reverse proxies
- Certain gateways
Explain that architecture varies and a DMZ is not the only modern design pattern.
Network Security for Small Businesses
Answer: “I don’t have an enterprise security team. What do I actually need?” Calculate your score with the Small Business Network Security Score and audit against our Small Business Cybersecurity Checklist.
Minimum Practical Security Stack
- Business-grade firewall/router
- MFA for important accounts
- Endpoint protection
- Automatic security updates
- Separate guest Wi-Fi
- Network segmentation where practical
- Secure DNS/web filtering
- Email protection
- Regular tested backups
- Centralized logging/alerts where practical
- Secure remote access
- Vulnerability and configuration reviews
How to Choose Network Security Tools
Evaluate tools based on:
- Security capabilities
- Network size
- Throughput
- Number of users/devices
- Cloud support
- Remote-work requirements
- Central management
- Logging
- Integration
- Automation
- Reliability
- Vendor support
- Scalability
- Training requirements
- Total cost of ownership
Use our interactive Security Tool Finder or browse our comprehensive catalog of over 110 free browser-based diagnostic utilities.
Before Buying a Firewall, Ask:
- What throughput do we actually need?
- Will encrypted traffic be inspected?
- Do we need IDS/IPS?
- Do we need site-to-site VPN?
- Remote-user VPN?
- High availability?
- Cloud management?
- SD-WAN?
- Application control?
- Centralized logs?
- Multiple offices?
When Should You Consider Managed Security Services?
A business may consider external security support when it lacks:
- 24/7 monitoring
- Security specialists
- Incident-response capability
- Firewall expertise
- Detection engineering
- Log analysis
- Vulnerability management resources
Questions to Ask an MSSP
- What exactly will you monitor?
- Is monitoring 24/7?
- What happens after an alert?
- What are response times?
- Who owns incident response?
- What logs are collected?
- How long are logs retained?
- What systems are supported?
- How are false positives handled?
- How will results be reported?
- What happens during a serious incident?
How to Build Network Security Step by Step
Step 1 — Inventory Your Assets
Identify: Users, Devices, Servers, Applications, Network equipment, Cloud services, Sensitive data.
Step 2 — Identify Critical Assets
Determine what would hurt most if compromised or unavailable.
Step 3 — Secure Identity
Use: Unique accounts, MFA, Least privilege, Admin-account separation.
Step 4 — Secure and Patch Devices
Update systems and remove unsafe configurations.
Step 5 — Configure Traffic Controls
Review: Firewall rules, Open ports, Internet-facing services, Remote access.
Step 6 — Segment the Network
Separate: Guests, Users, Servers, Administrators, Sensitive data, IoT where practical.
Step 7 — Encrypt Sensitive Communications
Use secure protocols.
Step 8 — Deploy Detection and Monitoring
Use logs, alerts, IDS/IPS/NDR or appropriate monitoring.
Step 9 — Protect and Test Backups
Backups should support actual recovery.
Step 10 — Prepare Incident Response
Know: Who investigates? Who isolates systems? Who communicates? Where are backups? How will operations recover?
Step 11 — Test Security
Use: Vulnerability assessments, Configuration reviews, Access reviews, Restore tests, Authorized security testing with our Business Network Security Assessment.
Step 12 — Improve Continuously
Security is not a one-time installation.
Network Security Best Practices Checklist
- Maintain an accurate device and asset inventory
- Use MFA
- Remove unused accounts
- Separate administrator accounts
- Apply least privilege
- Patch operating systems and network devices
- Replace unsupported systems
- Review firewall rules
- Close unnecessary ports
- Segment sensitive networks
- Separate guest Wi-Fi
- Secure remote access
- Encrypt sensitive communications
- Deploy endpoint protection
- Monitor important logs
- Investigate IDS/IPS alerts
- Scan for vulnerabilities
- Back up critical data
- Test backup restoration
- Maintain an incident-response plan
- Review access regularly
- Train users against phishing and credential theft
How Do You Know Whether Your Network Is Secure?
Ask the reader:
Asset Visibility
Do you know every device connected to your network?
Identity
Does every important account use MFA?
Privilege
Can normal users access administrator-level systems?
Segmentation
Could one compromised laptop directly reach every critical server?
Firewall
When were firewall rules last reviewed?
Patching
Are internet-facing systems current?
Monitoring
Would you notice an unusual administrator login tonight?
Detection
Are important security alerts actually investigated?
Backup
Have you successfully restored from your backup recently?
Response
Does the team know what to do if ransomware is detected?
Warning Signs That a Network May Be Compromised
- Unexpected login attempts
- New administrator accounts
- Unusual outbound traffic
- Sudden network slowdown
- Unknown devices
- Security tools being disabled
- Repeated IDS/IPS alerts
- Strange DNS requests
- Unexpected configuration changes
- Unusual access to sensitive servers
- Large unexplained data transfers
- Users being locked out
- Ransom notes or encrypted files
What Should You Do If You Suspect a Network Breach?
- Confirm and document the alert
- Escalate to the appropriate security/IT team
- Preserve relevant logs and evidence
- Contain affected accounts/devices where appropriate
- Prevent further unauthorized access
- Determine affected systems
- Remove the cause of compromise
- Reset compromised credentials where appropriate
- Patch exploited vulnerabilities
- Recover from known-good systems/backups
- Increase monitoring
- Review how the incident happened
Common Network Security Mistakes
Flat Network Architecture
Overly Broad Firewall Rules
Shared Administrator Accounts
No MFA
Default Credentials
Unpatched Firewalls and Routers
No Logging
Logs Are Collected but Never Reviewed
Guest and Corporate Devices Share One Network
Excessive Privileges
Security Tools Are Installed but Never Tested
Network Security Tools by Function
| Tool Category | Main Problem It Solves |
|---|---|
| Firewall | Unauthorized network connections |
| IDS | Suspicious traffic detection |
| IPS | Detection + prevention |
| NDR | Network behavior analysis |
| NAC | Device/user network access |
| VPN | Protected remote/site connectivity |
| ZTNA | Granular application/resource access |
| EDR | Endpoint attack detection and response |
| SIEM | Centralized security telemetry and analysis |
| DNS Security | Malicious-domain access |
| Secure Web Gateway | Web traffic control |
| DLP | Sensitive-data exposure |
| Vulnerability Scanner | Known weaknesses |
| Configuration Management | Security configuration consistency |
Network Security Fundamentals by Business Size
Home / Very Small Office
Priority: Secure router, Strong Wi-Fi, Updates, MFA, Endpoint protection, Backups.
Small Business
Add: Business firewall, Guest segmentation, Central device management, Email security, Logging, Secure remote access, Vulnerability reviews.
Growing Organization
Add: NAC, IDS/IPS, Stronger segmentation, SIEM, Identity governance, Central monitoring, Formal incident response.
Enterprise
Potentially add: Zero Trust architecture, Advanced NDR, Microsegmentation, Security automation, Dedicated SOC, Advanced identity controls, Threat intelligence, Continuous security validation.
Network Security Fundamentals FAQ
What are network security fundamentals?
Network security fundamentals are the core principles, processes, architectural controls, and technologies used to protect networks, systems, communications, and data from unauthorized access, misuse, disruption, and attack. They include identity security, access control, firewalls, segmentation, secure communication, vulnerability management, threat detection, monitoring, incident response, and recovery.
What are the three pillars of network security?
The commonly recognized foundational security objectives are: Confidentiality, Integrity, and Availability, collectively known as the CIA triad.
What are the five pillars of network security?
There is no universal five-pillar network-security standard. Older NIST CSF 1.1 used five cybersecurity functions: Identify, Protect, Detect, Respond, and Recover. NIST CSF 2.0 now uses six: Govern, Identify, Protect, Detect, Respond, and Recover. CISA’s Zero Trust maturity model separately uses five technology pillars: Identity, Devices, Networks, Applications and Workloads, and Data.
What are the four types of network security?
There is no universally required list of exactly four. Network security usually involves multiple types of controls, including: Access control, Firewalls, Segmentation, IDS/IPS/NDR, Encryption, Endpoint protection, Secure remote access, Monitoring, Vulnerability management. It is more accurate to think in terms of layers of security controls than a fixed number.
What are the five fundamentals of security?
There is no single universal five-item definition. A widely accepted foundational model is the CIA triad: Confidentiality, Integrity, Availability. Modern security programs also use principles such as least privilege, defense in depth, strong authentication, continuous monitoring, and risk management.
What are the 5 C’s of security?
“5 C’s of security” is not a universally standardized network-security framework. Different industries and authors may use the phrase differently. For network-security fundamentals, established concepts such as the CIA triad, least privilege, defense in depth, Zero Trust, and recognized cybersecurity frameworks provide a more reliable foundation.
What does a firewall do?
A firewall controls network traffic according to security policies and rules. It can allow legitimate connections while blocking prohibited or suspicious connections.
What is the difference between IDS and IPS?
An IDS primarily detects suspicious activity and generates alerts. An IPS is positioned to detect and actively prevent or block certain malicious traffic.
Do I still need a firewall if I use antivirus?
Yes, they solve different problems. A firewall primarily controls network communications, while antivirus/endpoint protection focuses on malicious activity affecting individual systems. A layered security strategy commonly uses both.
What is network segmentation?
Network segmentation divides a network into smaller zones and controls communication between them. Its purpose includes reducing unnecessary access and limiting how far an attacker can move after compromising one system.
Is Zero Trust part of network security?
Yes. Zero Trust principles can significantly influence network architecture and access decisions by reducing implicit trust and enforcing more granular, policy-based access.
Are VLANs Layer 2 or Layer 3?
A VLAN primarily provides logical segmentation at Layer 2. Communication between different VLANs normally requires Layer 3 routing.
Is BGP Layer 2 or Layer 3?
BGP is not a Layer 2 switching protocol. It exchanges routing information for IP networks and runs over TCP.
Is network security difficult to learn?
Network security becomes easier to understand when the learner first understands basic networking concepts such as IP addressing, routing, switching, ports, TCP/UDP, DNS, and the OSI/TCP-IP models. Hands-on practice in authorized lab environments can then help connect networking concepts with security controls.
What skills are useful for network security?
Useful foundational skills include: TCP/IP, Routing, Switching, DNS, Firewalls, Linux/Windows basics, Identity and access management, Log analysis, Vulnerability management, Security monitoring, Troubleshooting. This should remain a short FAQ answer rather than becoming a career guide.
What are the seven layers of networking?
The OSI model contains: Physical, Data Link, Network, Transport, Session, Presentation, Application. Network-security controls can operate across several of these layers.
How can a small business improve network security?
Start with the controls that reduce the most common risks: Maintain an asset inventory, Use MFA, Patch systems, Use a properly configured firewall, Separate guest access, Protect endpoints, Secure remote connections, Back up critical data, Monitor important events, Create an incident-response plan.
Final Takeaway
Start by identifying what you need to protect. Then determine:
- Who should access it?
- From which devices?
- Through which network paths?
- What should be blocked?
- What should be monitored?
- What happens if a control fails?
When those questions have clear answers and the controls are tested regularly, network security becomes a manageable system rather than a collection of disconnected security products.
Explore more guides: Network Security Knowledge Base • Interactive Security Utilities
Share This Network Security Guide
Help IT professionals, network engineers, and students strengthen their cyber defense.
Zubayer Hasan
LinkedIn Profile →Md Zubayer AL Hasan is the lead cybersecurity platform architect and security researcher at SafeNetworkHub. Dedicated to zero-knowledge cryptography, infrastructure vulnerability auditing, and building accessible privacy tools.
Appreciate this post. Will try it out.